This content is viewable by Everyone
News
CrowdStrike Falcon replacing Symantec and Trellix
-
Author: ANGELA WOON
- Date:
- Associated Services:
UCSF is strengthening its defenses against advanced cyber threats. Beginning Sept. 23, 2026, UCSF is transitioning to CrowdStrike Falcon, a next-generation endpoint security solution that will replace Symantec Endpoint Protection (SEP) and Trellix (formerly known as FireEye).
CrowdStrike Falcon will provide a consolidated security solution that uses fewer resources, resulting in improved system performance and faster cyberattack containment with less disruption to your work.
What is changing?
UCSF IT will begin by installing CrowdStrike Falcon sensor on all IT-managed workstations, including desktops and laptops. During the transition:
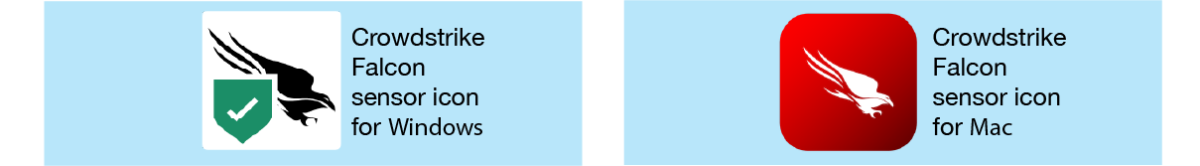
- You may notice the following CrowdStrike Falcon sensor installed on your computer:
- CrowdStrike Falcon will temporarily coexist with SEP and Trellix.
SEP and Trellix will be removed after the CrowdStrike Falcon installation is complete. Newly provisioned computers will be preloaded with CrowdStrike Falcon.
What do I need to do?
If you are on an IT-managed computer, you may be prompted to reboot after UCSF IT installs CrowdStrike Falcon and removes SEP and Trellix; please do so to ensure optimal CrowdStrike performance.
The UCSF IT Cybersecurity team will connect with users of department-managed or non-IT-managed devices (BYOD), as well as server managers, after completing the IT-managed device rollout (most likely in November). CrowdStrike for BYOD and partner IT-managed systems will likely be available in early 2027; until then SEP and Trellix will continue to function and provide appropriate protections.
Learn more about Endpoint protection.
Need support?
If you encounter any issues with CrowdStrike Falcon, please open a ServiceNow ticket.
- Owning Team: Cybersecurity
-
Team Lead: Patrick Phelan